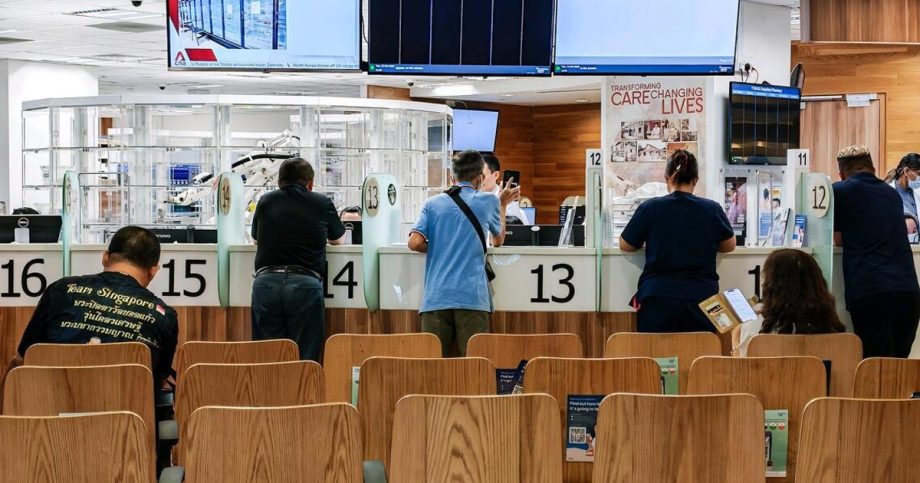
SINGAPORE – A “preventable lapse” involving a missed security update to a shared domain name system led to a 9½-hour public healthcare service outage on Oct 13, Parliament heard.
Affected services included appointment bookings, visitor registration, medication dispensing and billing, Senior Minister of State for Health Tan Kiat How said on Nov 3.
He added that about 4,000 outpatient appointments were rescheduled, and some patients experienced delays of up to two hours. There were, however, no reported adverse incidents affecting patient safety as a result of the disruption.
The outage affected all three of Singapore’s public healthcare clusters – NHG Health, National University Health System and SingHealth.
“This was a known change and a preventable lapse,” Tan said, replying to questions from MPs over the cause and extent of the disruption, which was the longest in recent years.
MPs Joan Pereira (Tanjong Pagar GRC) and Poh Li San (Sembawang West) asked about the reason for the disruption and whether backup systems were in place, while Dennis Tan (Hougang) asked whether measures had been implemented to reduce the risk of such systemwide disruptions.
Tan Kiat How said the disruption occurred because the required security update to a shared domain name system (DNS) service was not completed before a scheduled global change.
DNS works like an address book, transforming website addresses into numerical IP addresses, which systems use to locate and connect to applications.
Tan said that while national health-tech agency Synapxe had contracted a service provider to manage the necessary update, it was not carried out. Synapxe is reviewing the provider’s contractual obligations and will take appropriate action for any established lapses, he added.
“Regardless of the outsourcing arrangement, Synapxe remains accountable for the resilience of its critical systems,” he said.
He reiterated that the incident was not the result of a cyberattack and that there was no unauthorised access to patient data, which was not compromised or lost.
Read Full Article At Source